📊 Full opportunity report: Leveraging Quantum Risk Monitoring For Enhanced Cyber Defense on IdeaNavigator AI — validation score, market gap, and execution plan.

Get smart everyday buys delivered free — and shop member deals
- Fast, free delivery on millions of items
- Access to Prime Big Deal Days deals on October 6–7
- Prime Video, Amazon Music and more included
TL;DR
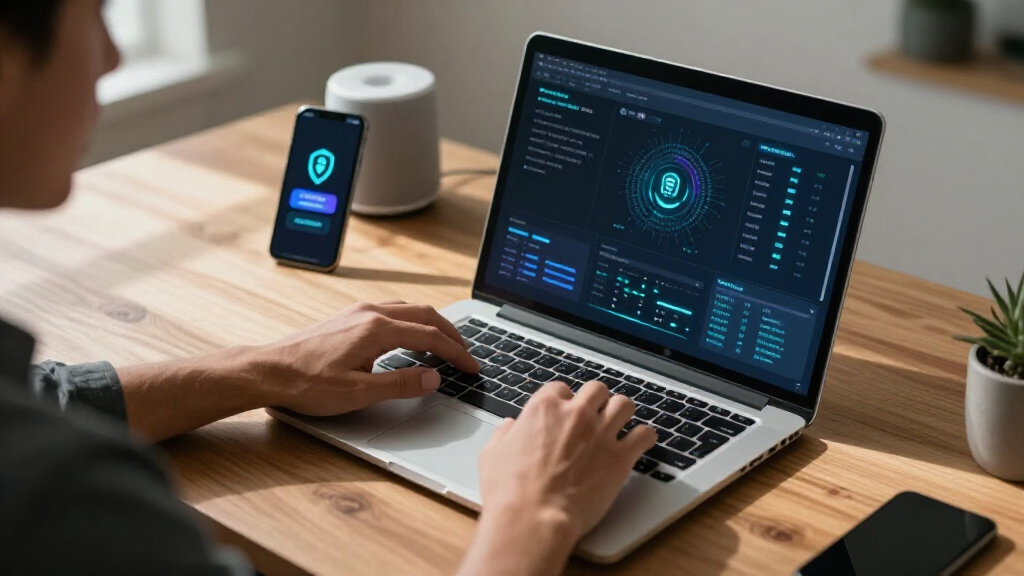
A new quantum risk monitoring approach is being tested by regulated organizations to identify quantum-vulnerable assets. This initiative aims to improve visibility, compliance, and migration planning ahead of upcoming standards and deadlines. The development is still in early testing phases with pilot programs underway.
Enterprises in regulated sectors are actively testing a new quantum risk monitoring system designed to identify cryptographic assets vulnerable to quantum attacks. This development aims to help organizations comply with upcoming standards and deadlines, and to better understand their exposure to long-term data decryption risks. The initiative is driven by recent regulatory mandates and the need for improved visibility into cryptographic inventories.
The quantum risk monitor being tested by early adopters is an agentless discovery scanner combined with lightweight host sensors. It passively fingerprints TLS endpoints, scans filesystems and binaries for cryptographic libraries, and flags quantum-vulnerable algorithms such as RSA and elliptic-curve cryptography (ECC). The system scores assets based on their sensitivity, data lifetime, and potential exposure to ‘harvest-now-decrypt-later’ threats, then exports a cryptographic bill of materials (CBOM) and a prioritized migration roadmap aligned with NIST’s post-quantum cryptography standards (FIPS 203/204/205).
According to an anonymous researcher involved in the development, the primary goal is to provide organizations with accurate, continuously updated inventories of cryptographic assets, which are currently difficult to track across large, complex IT environments. This visibility is critical for prioritizing migration efforts, demonstrating regulatory compliance, and quantifying long-term risks, especially as the June 2026 U.S. Executive Order sets strict deadlines for PQC adoption by December 2030 for key establishment and December 2031 for signatures.
Implications for Regulatory Compliance and Cyber Resilience
This development is significant because it addresses a key challenge faced by large organizations: the lack of comprehensive visibility into their cryptographic assets. Without an accurate inventory, organizations cannot effectively prioritize migration efforts or demonstrate compliance with upcoming mandates. The ability to identify and score vulnerabilities in real time enhances cyber resilience by enabling proactive mitigation of quantum threats, which could otherwise compromise sensitive data long after current encryption methods become obsolete.
Furthermore, early testing of these tools could accelerate industry-wide adoption of crypto-agility practices, reducing the risk of costly breaches and regulatory penalties. As the adoption of post-quantum cryptography becomes mandatory, organizations equipped with such monitoring systems will be better prepared to meet deadlines and manage transition risks efficiently.
As an affiliate, we earn on qualifying purchases.
Regulatory Push and Growing Quantum Threat Landscape
The push for quantum risk monitoring comes amid the recent finalization of the first PQC standards by NIST in August 2024, which establish a framework for transitioning to quantum-resistant cryptography. The U.S. government’s June 2026 Executive Order emphasizes the urgency of this transition, setting hard deadlines for PQC key establishment and signatures. Organizations in sectors like banking, healthcare, defense, and critical infrastructure are under increasing pressure to comply and demonstrate cryptographic readiness.
Until now, most enterprises have lacked the tools to accurately inventory their cryptographic assets or assess their vulnerability to quantum attacks. This gap has created a pressing need for automated, scalable solutions that can provide real-time visibility and support migration planning. Early pilot programs with quantum risk monitors aim to fill this gap, with initial results indicating organizations are often surprised by the extent of their undiscovered vulnerable assets.
As an affiliate, we earn on qualifying purchases.
Uncertainties Around Deployment and Effectiveness
It is not yet clear how widely adopted these quantum risk monitoring tools will become beyond initial pilots. The effectiveness of passive fingerprinting and asset scoring in complex, heterogeneous environments remains to be validated at scale. Additionally, questions remain about the integration of these tools with existing security workflows and their ability to keep pace with evolving threat landscapes and cryptographic standards.
Further, the timeline for full deployment across large organizations and the actual impact on migration speed and regulatory compliance are still uncertain, as pilot programs are in early stages and results are preliminary.
cryptographic asset inventory scanner
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Next Steps for Broader Adoption and Validation
The immediate next step is for participating organizations to complete their pilot scans and assess the accuracy and completeness of the inventories generated. Success in these pilots could lead to wider deployment and integration into enterprise security frameworks. Industry groups and regulators may also begin endorsing or mandating the use of such tools as part of compliance requirements.
In parallel, vendors are expected to refine their solutions, adding features like continuous monitoring, automated reporting, and migration advisory services. The broader cybersecurity community will watch closely to see if early pilot results translate into effective, scalable solutions capable of meeting the 2030-2031 PQC deadlines.
quantum vulnerability detection tools
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Key Questions
What is a quantum risk monitor?
A quantum risk monitor is a tool that passively scans and fingerprints cryptographic assets across an enterprise to identify vulnerabilities related to quantum computing threats. It helps organizations inventory, score, and plan migration efforts for cryptographic systems vulnerable to quantum attacks.
Who should use this technology?
It is primarily intended for CISOs, cryptography/PKI leads, and GRC teams in regulated sectors such as banking, healthcare, defense, and critical infrastructure, especially those subject to PQC migration mandates.
When will organizations need to fully migrate to PQC?
The U.S. government has set deadlines for PQC key establishment by December 31, 2030, and for signatures by December 31, 2031. Organizations should begin assessing their vulnerabilities now to meet these deadlines.
Are these tools effective right now?
Early pilot results suggest they are effective at identifying previously unknown vulnerable assets, but full-scale validation and integration into enterprise workflows are still underway.
What are the main challenges in adoption?
Challenges include integrating the tools with existing security systems, scaling the discovery process in large environments, and ensuring timely migration to meet regulatory deadlines.
Source: IdeaNavigator AI
Fall Picks
fall essentials
As an affiliate, we earn on qualifying purchases.